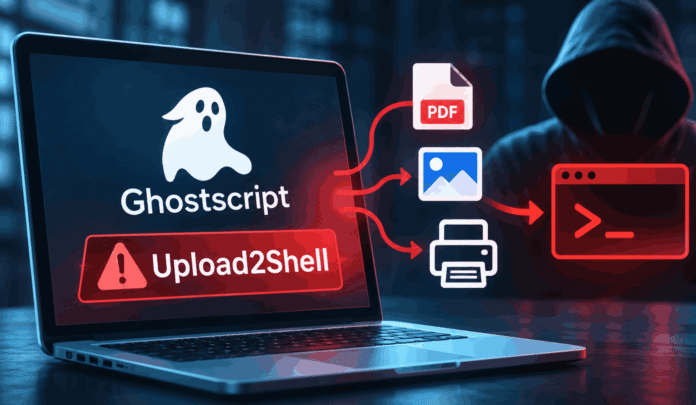
A seemingly harmless file upload could give attackers a way into a server. A newly disclosed Ghostscript vulnerability, tracked as CVE 2026 125396 and nicknamed Upload2Shell, highlights how dangerous ordinary document processing can become when a security boundary fails.
The vulnerability allows malicious PostScript and PDF files to escape Ghostscript’s security sandbox and execute commands on the system running the document conversion process. This creates a serious risk for organisations that accept files through public websites, email services and shared printing infrastructure.
Security researchers at autonomous penetration testing company pwn.ai demonstrated how the issue could be exploited through several commonly used applications. The affected environments include Debian 13, Roundcube, Plesk, MediaWiki and multiple WordPress plugins.
The problem is particularly concerning because Ghostscript often operates behind the scenes. It is widely used to process and convert documents and is integrated into tools such as ImageMagick, Pillow and PHP’s Imagick. As a result, applications that appear to accept ordinary image formats may still send uploaded files through Ghostscript during processing.
That means attackers may not need to upload a file with an obvious PostScript or PDF extension. A file presented as an image could also become a potential attack vector if the server’s conversion pipeline routes it through the vulnerable software.
VulnCheck, which acts as a CVE Numbering Authority, assigned the vulnerability a CVSS 4.0 score of 8.5, placing it in the high severity category.
The flaw is a use after free vulnerability in Ghostscript’s Type 1 font loading process. It involves the .putgstringcopy procedure in the gs_fonts.ps file, which uses a privileged operation called .forceput without properly validating its input types.
Researchers found that a specially crafted document could trigger a type error and catch it using its own error handling routine. This sequence could leave an attacker with access to a privileged operation that should not be available to untrusted documents.
The resulting memory corruption can provide a write what where primitive. In practical terms, this gives an attacker a way to modify sensitive memory locations and interfere with the protections enforced by Ghostscript’s -dSAFER sandbox.
Once those protections are bypassed, an attacker may be able to execute commands with the permissions of the application processing the document.
Artifex addressed the underlying issue in Ghostscript 10.08.0, released on September 8, 2026. The fix was developed with contributions from Artifex engineer Ken Sharp.
Which Systems Are Vulnerable and Where Have Patches Arrived?
The research from pwn.ai demonstrates that Upload2Shell is not limited to a single application or operating system. Its impact depends heavily on how software uses Ghostscript to process documents and images.
Among the confirmed attack scenarios, researchers demonstrated command execution through anonymous IPP print jobs on Debian 13. The attack ran commands under the permissions of the lp account.
Roundcube was another affected application. A malicious email from an external sender could trigger code execution when the recipient opened it, provided the tested ImageMagick configuration was in place. The demonstrated attack affected Roundcube 1.7.2 and executed commands as www-data.
Other confirmed targets included Forminator 1.55.1, Essential Addons for Elementor Lite 6.7.0, MediaWiki 1.46.0, DokuWiki 2026-07-14a, Mayan EDMS 4.11.5 and ResourceSpace 11.0.
Plesk Obsidian 18.0.79 was also included in the research. Its bundled Roundcube installation and older Ghostscript version created an exploitable path. Researchers demonstrated command execution as roundcube_sysuser. However, they noted that AppArmor prevented the shell from running in one test environment.
WordPress requires a separate explanation. Its exposure was addressed through CVE 2026 65640, which was fixed in WordPress 7.0.4 on August 12, 2026. The vulnerability requires an account with the upload_files capability, which Author accounts and higher generally possess by default. The attack also depends on the presence of Imagick and Ghostscript on the server.
Researchers also reported reaching Ghostscript 10.05.0 inside Google’s document rendering infrastructure. They demonstrated native control of the rendering process and accessed the worker’s /proc/version file. However, they did not claim to have obtained a complete shell. Google reportedly mitigated the affected path on November 10.
Patch availability remains uneven across Linux distributions.
As of November 22, 2026, Debian 13, Ubuntu, Arch Linux, Alpine, Gentoo and openSUSE Tumbleweed have shipped fixes. Windows, macOS distributions through Homebrew and MacPorts, and FreeBSD are also listed as fixed.
Debian 12 remains vulnerable according to the available tracking information. Red Hat Enterprise Linux still has an open tracking issue, while Amazon Linux 2 and Amazon Linux 2023 are awaiting a published fix.
SUSE Linux Enterprise and openSUSE Leap 16 are also listed as affected or undergoing remediation.
Administrators should be careful when checking version numbers. A distribution can backport a security fix without upgrading Ghostscript to version 10.08.0. For example, Ubuntu 24.04 LTS has a fixed package based on Ghostscript 10.02.1, while Ubuntu 22.04 LTS has a corrected package based on version 9.55.0.
Consequently, checking only the output of the gs –version command will not establish whether a system is protected. Distribution specific security advisories and package revisions provide a more reliable indication.
Is Upload2Shell Being Exploited? What Should Administrators Do?
Despite the seriousness of the findings, there is currently no confirmed public report of attackers exploiting CVE 2026 125396 in the wild. The vulnerability is also absent from CISA’s Known Exploited Vulnerabilities catalogue.
Its EPSS score stood at 0.0013 following disclosure, indicating a relatively low estimated probability of exploitation at that point. However, this should not be interpreted as a reason to delay security updates.
Pwn.ai has released a self contained PostScript proof of concept demonstrating memory corruption in the vulnerable renderer. The published sample does not execute a shell or access files on the host system. It also fails against the fixed Ghostscript 10.08.0 release.
The complete command execution chains have not yet been made publicly available. Researchers have indicated that they plan to publish a detailed case study covering the Debian 13 CUPS attack.
That disclosure could make it easier for other security researchers and attackers to reproduce the technique. Organisations running exposed print servers and document conversion services should therefore treat patching as a priority.
The first step is to install the security update provided by the relevant operating system vendor. Where an official package is unavailable, administrators should assess whether upgrading to a supported, fixed Ghostscript release is possible.
They should also restart services that may keep vulnerable converter processes running, including CUPS, PHP FPM, document preview services and background processing workers.
Package versions can be checked using the following commands:
Debian and Ubuntu:
dpkg -l ghostscript
RPM based Linux distributions:
rpm -q ghostscript
These results should be compared against the relevant vendor advisory rather than relying exclusively on the upstream version number.
Another important consideration is software running inside containers. Updating Ghostscript on the host machine does not automatically fix an older copy bundled inside a Docker image or application package. Organisations should inspect their container images, rebuild affected environments and redeploy updated versions.
WordPress administrators should install WordPress 7.0.4 or a later fixed release, while also checking whether their current branch has received the relevant security backport. Roundcube users should upgrade to a release containing the CVE 2026 114727 hardening changes, which restrict the attachment types sent for image conversion.
Where immediate patching is not possible, administrators can reduce exposure through several additional precautions:
- Require authentication before users can submit jobs to shared printing queues.
- Validate the actual contents of uploaded files instead of trusting their extensions or declared MIME types.
- Prevent document rendering processes from launching shells or unnecessary system commands.
- Restrict the file formats and document types that applications are allowed to send to Ghostscript.
Security controls such as AppArmor can also help limit the damage caused by a successful sandbox escape. However, these measures should be treated as additional protection rather than a replacement for installing the security update.
Upload2Shell is a reminder that file conversion software can become a serious entry point into otherwise protected infrastructure. An application does not need to offer direct command execution to become vulnerable. If it processes attacker controlled documents through an unsafe rendering component, that component can become the weakest link.
With multiple confirmed attack paths and incomplete patch coverage across some Linux distributions, administrators should review their document processing infrastructure now rather than waiting for public exploit code to appear.
Follow TechBSB For More Updates